Top CMMC Compliance Services in Global
Compare 33 verified CMMC specialists serving Global. From consultants to certification bodies, find the right partner for your compliance journey. As of October 2026, ISMS Directory lists 33 verified providers for this search, ranked by real 30-day buyer demand on the directory (not paid placement).
Showing 33 services
Thoropass
End-to-end compliance platform combining AI-powered automation with in-house audit services from Big 4 trained experts.
Service Type
Regions
I.S. Partners
Philadelphia CPA and compliance firm for SOC, HIPAA, HITRUST, PCI, and ISO 27001 assessments.
Service Type
Regions
heygrc
GitHub App that reviews every pull request against your compliance frameworks, flags changes that put a control at risk, and says exactly what to fix.
Service Type
Regions

Lazarus Alliance
US assessor for SOC 2, FedRAMP, CMMC, and related federal-adjacent security audits.
Matched on: CMMC · Global
Why am I seeing this? An independent provider, selected by coverage match and 30-day directory demand. No vendor can pay for this spot.
URM Consulting
UK information security consultancy for ISO 27001 implementation, internal audit, and certification support with a large public track record.
Service Type
Regions
BARR Advisory
Cloud-native compliance firm offering SOC 2 audits and ISO 27001 certification with coordinated multi-framework programs for SaaS.
Service Type
Regions
CyberSaint
Boston cyber GRC platform (CyberStrong) for NIST-oriented risk, control testing, and vendor risk.
Service Type
Regions
Auro Security
Most modern product teams, including SaaS, FinTech and cloud-native startups are moving fast, building with AI, and operating in an environment where enterprise buyers, regulators, and investors expect real security. Auro Security exists to help those teams get there. Operating across India and the Middle East, we work with founders, CTOs, and compliance leads to build security programs that hold up under scrutiny, not just on paper. What We Do We offer a focused suite of cybersecurity services: - SOC 2 and ISO 27001 Compliance: End-to-end audit readiness, gap assessments, policy creation, evidence collection support, and continuous monitoring. - VAPT (Vulnerability Assessment and Penetration Testing): Deep technical testing for web apps, mobile apps, APIs, cloud infrastructure, and networks to uncover risks before attackers do. - vCISO Services: Fractional cybersecurity leadership to help you build a security roadmap, manage risk, and meet enterprise expectations as you scale. Who We Serve We primarily work with: SaaS companies and cloud-native startups, FinTech and payments platforms, early-stage teams preparing for enterprise sales or compliance audits.
Service Type
Regions
Withum
US CPA firm with a technology attestation practice frequently used for SOC 2 by SaaS companies.
Service Type
Regions
Strike Graph
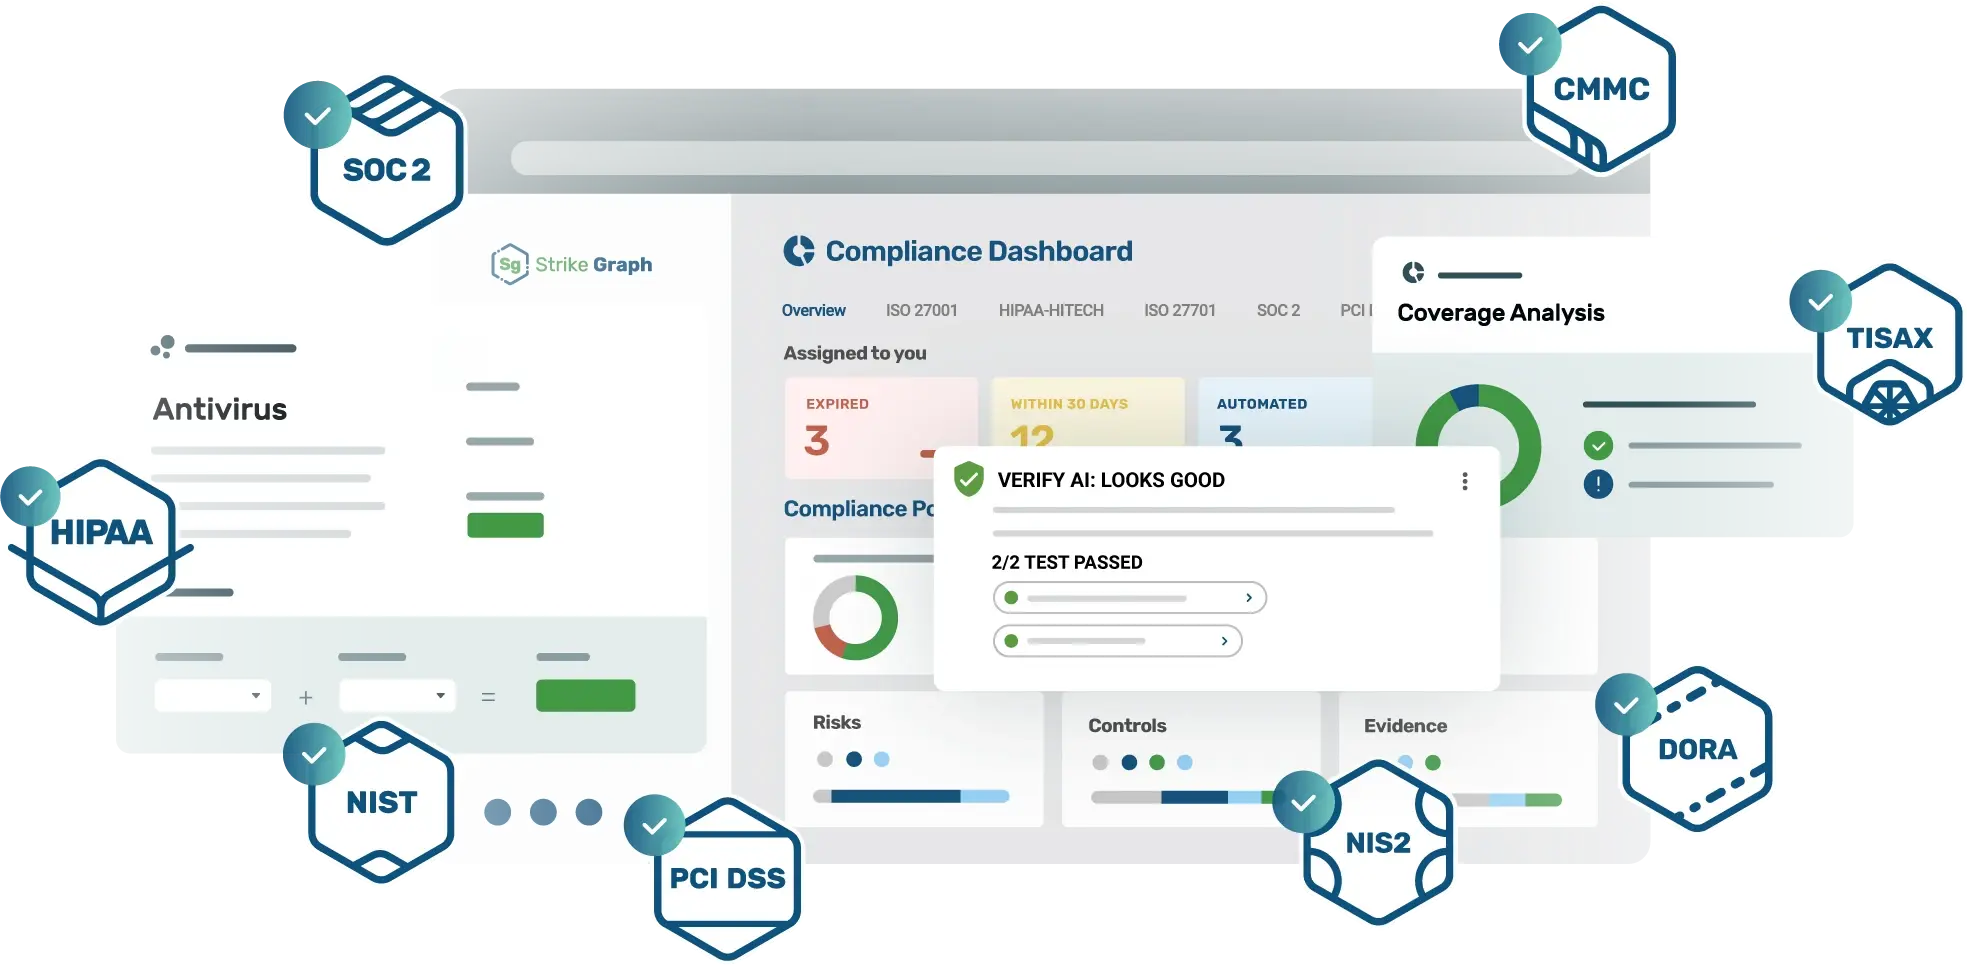
AI-native compliance management platform that accelerates audits and eliminates redundant work across 5,000+ data source integrations.
Service Type
Regions
ISMS Copilot Model API
OpenAI-compatible text-only compliance completions: curated framework knowledge (100+ modules) injected before generation and disclosed on success.
Service Type
Regions
Secureframe
AI-powered GRC platform that automates compliance, mitigates risk, and builds customer trust through expert-backed automation.
Service Type
Regions
A-LIGN
High-volume multi-framework audit firm for SOC 2, ISO 27001, HITRUST, FedRAMP, CMMC, and PCI, with dual ANAB/UKAS ISO pathways.
Service Type
Regions
Scytale
AI-powered compliance automation platform with dedicated human experts, supporting 60+ security and privacy frameworks.
Service Type
Regions
Hyperproof
Intelligent GRC platform that transforms compliance from a cost center into a competitive advantage with AI-powered automation.
Service Type
Regions
KirkpatrickPrice
Nashville licensed CPA firm for SOC 2, PCI, HIPAA, and ISO 27001 audits across US offices.
Service Type
Regions
Carbide
Canadian security and privacy management platform combining software automation with expert advisory for fast-growing companies.
Service Type
Regions
ISMS Copilot Account MCP
Talk to a specialist compliance AI from the harness you already use. Hosted remote MCP server (HTTP, Streamable HTTP) for Claude Code, Cursor, Codex, or any MCP client.
Service Type
Regions
Coalfire
Enterprise cybersecurity and compliance assessment firm for FedRAMP, SOC 2, HITRUST, PCI, ISO 27001, and government frameworks.
Service Type
Regions
Tevora
Irvine cybersecurity and compliance firm for PCI, SOC 2, ISO 27001, HITRUST, CMMC, and FedRAMP.
Service Type
Regions
CBIZ Pivot Point Security
US information security consultancy specializing in ISO 27001 implementation, SOC 2 readiness, CMMC, and ongoing compliance programs.
Service Type
Regions
Diligent
New York governance platform covering board, audit, risk, and compliance workflows for enterprises.
Service Type
Regions

Onspring
Kansas City no-code GRC platform for risk, compliance, audit, policy, and third-party workflows.
Service Type
Regions

OneTrust
Atlanta GRC and privacy platform for privacy, third-party risk, and compliance programs at enterprise scale.
Service Type
Regions
Ostendio
Washington DC security and compliance platform for assessments, vendor risk, and control programs.
Service Type
Regions
ISMS Copilot
Compliance AI engine for 75+ frameworks including ISO 27001, SOC 2, GDPR, NIS2, DORA, and ISO 42001. Chat for practitioners. OpenAI-compatible API and embed for products and partners.
Service Type
Regions
Schellman
Leading US IT compliance attestation firm for SOC 1/2/3, PCI, and ANAB-accredited ISO certifications including ISO 27001 and ISO 42001.
Service Type
Regions

BitSight
Boston security-ratings platform used in third-party risk and cyber underwriting programs.
Service Type
Regions
ControlCase
US QSA and assessor for PCI DSS, SOC 2, ISO 27001, and related payment-security programs.
Service Type
Regions
Vanta
AI-powered trust management platform that automates compliance, manages risk, and builds customer trust across 35+ frameworks.
Service Type
Regions
Scrut Automation
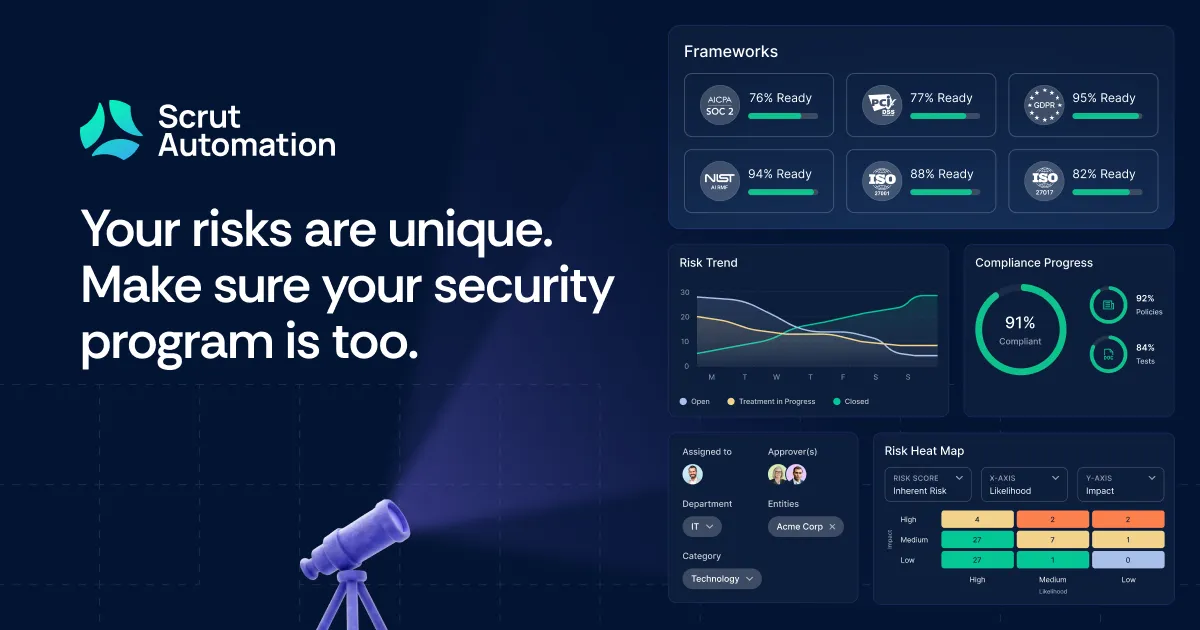
Scrut Automation simplifies continuous compliance automation for cloud-native companies.
Service Type
Regions
Insight Assurance
Florida CPA firm providing SOC 2, ISO 27001, and HIPAA attestation for mid-market technology companies.
Service Type
Regions
Apptega
Atlanta continuous-compliance platform built for MSSPs and security teams running multi-framework programs.
Service Type
Regions