
ContrailRisks
ContrailRisks is a Berlin-based strategic advisory firm delivering lean, high-impact cybersecurity & risk management solutions. We help businesses identify vulnerabilities, implement tailored strategies, and enhance operations—minimizing risks, reducing costs, and boosting resilience.
About
ContrailRisks delivers lean, high-impact cybersecurity services tailored for startups and growing businesses. We prioritize strategic alignment, regulatory readiness, and practical outcomes over checkbox compliance. Our expertise in EU regulations and global standards enables effective, business-focused security support. What frameworks or standards are your services focused on? Our services align with ISO/IEC 27001:2022, NIST CSF 2.0, DORA, NIS2, IEC 62443, CMMC, Secure Control Framework (SCF), and CIS Controls. We guide clients in selecting the most appropriate framework based on their sector, maturity, and regulatory needs. How does pricing work for your offers? We offer fixed-fee packages for assessments and implementations, monthly subscriptions for vCISO services, and discounted starter packs for early-stage companies. Pricing is transparent and tailored to the client’s size, complexity, and requirements.
Problems They Solve
Industry Specialization
Target Client Size
Supported Languages
View ContrailRisks public scorecard
Live demand signals, peer comparison, and coverage gaps - updated every 15 minutes from ISMS Directory traffic.
Interested in ContrailRisks?
Visit their website to learn more about their services and get started.
Visit ContrailRisksExplore More
Related Services
MeasurementPros - Implementation and Assurance
MeasurementPros brings hands-on implementation experience across security (ISO 27001, SOC 2) and governance (DORA, NIS2, CRA, EU AI Act, AIUC-1, GDPR, vCISO), serving clients in the EU as well as North American companies exposed to EU law.
Bitsecura
*** Helping Businesses Achieve Compliance & Certification Success *** Bitsecura is a IT governance, risk, and compliance (GRC) firm specialising in helping organisations protect their critical assets, navigate complex regulatory landscapes, and build sustainable cybersecurity frameworks. With over 20 years of industry experience, we offer strategic guidance, bespoke solutions, and operational support that align seamlessly with your business objectives. Our commitment to practical innovation and long-term partnerships ensures that working with Bitsecura not only strengthens your current security posture, but also builds a lasting foundation for future resilience.
i.s.c. Group
ISMS implementations, OneCompliance(tm) program to implement multiple standards at once.

SrivelEnterprise
A seasoned professional with 17+ years of fruitful experience with expertise in ISO Certification, SSAE18 (SOC1 and SOC2), GDPR, Quality Management System (ISO 9001), Information Security Management System (ISO 27001), Information Technology Service Management System (ISO 20001), Asset Management System (ISO 55001), HIPAA, Certified Data Protection Officer, Business Continuity, VAPT, Risk Management, Secure Coding, Data Privacy, Processing Integrity, E-learning, Training and Mentoring, Design Thinking, Operations, Strategy, People Management, Technocommercial Acumen. Management Systems: Effectively implemented, maintained, audited ISO 9001 (QMS), ISO 27001 (ISMS), ISO 23001 (BCMS), ISO 20001 (ITSM), ISO 27701 (PMS), ISO 42301 (AIMS), CMMI, SSAE18 (SOC1, SOC2), HIPAA, HITRUST, HITECH, CCPA, GDPR, FedRAMP standards in various organizations across industries. Strong understanding of business best practices w.r.t. quality, information security, continuous process improvements.
Auro Security
Most modern product teams, including SaaS, FinTech and cloud-native startups are moving fast, building with AI, and operating in an environment where enterprise buyers, regulators, and investors expect real security. Auro Security exists to help those teams get there. Operating across India and the Middle East, we work with founders, CTOs, and compliance leads to build security programs that hold up under scrutiny, not just on paper. What We Do We offer a focused suite of cybersecurity services: - SOC 2 and ISO 27001 Compliance: End-to-end audit readiness, gap assessments, policy creation, evidence collection support, and continuous monitoring. - VAPT (Vulnerability Assessment and Penetration Testing): Deep technical testing for web apps, mobile apps, APIs, cloud infrastructure, and networks to uncover risks before attackers do. - vCISO Services: Fractional cybersecurity leadership to help you build a security roadmap, manage risk, and meet enterprise expectations as you scale. Who We Serve We primarily work with: SaaS companies and cloud-native startups, FinTech and payments platforms, early-stage teams preparing for enterprise sales or compliance audits.
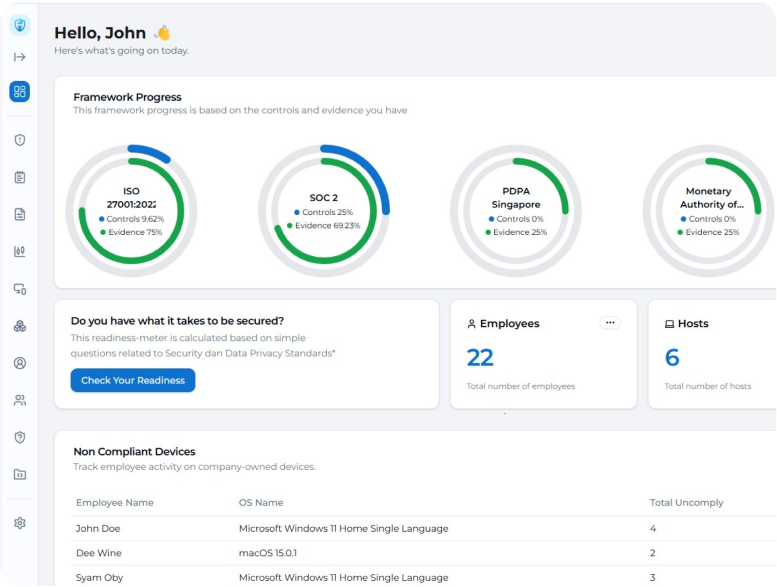
FEHA
FEHA is an AI and Human powered platform supporting businesses to comply with various frameworks and regulations, and prepare for certification, seamlessly.
The ISO Guys 27001, 27701 , 42001
At Cybercontrols we understand the ever-growing threat landscape of the digital world. Our mission is to provide comprehensive cyber security services that protect your digital frontiers.
URM Consulting
UK information security consultancy for ISO 27001 implementation, internal audit, and certification support with a large public track record.