Beste Berater für Gesundheitswesen
Browse 10 verified consultants with deep expertise in the healthcare sector. Get compliance help from specialists who understand your industry. As of October 2026, ISMS Directory lists 10 verified providers for this search, ranked by real 30-day buyer demand on the directory (not paid placement).
Zeige 10 Dienste

SolidInfoSec
Information security consulting focused on strengthening governance, risk and compliance practices. We help organizations structure and implement practical security processes, support audit readiness and build sustainable frameworks that remain workable over time.
Service Type
Regions
MeasurementPros - Implementation and Assurance
MeasurementPros brings hands-on implementation experience across security (ISO 27001, SOC 2) and governance (DORA, NIS2, CRA, EU AI Act, AIUC-1, GDPR, vCISO), serving clients in the EU as well as North American companies exposed to EU law.
Service Type
Regions
MatrixGard
Fractional DevSecOps for pre-seed and seed startups: SOC 2, ISO 27001 and DPDP Act readiness, cloud security and AWS hardening, delivered by the engineer who does the work. Readiness and remediation, not attestation. Remote, worldwide.
Service Type
Regions

Genius GRC
We offer cybersecurity and compliance consulting that focuses on delivering high quality service at a reasonable price. ISO 27001, SOC 2, ISO 42001, GDPR
Matched on: Consulting · Healthcare
Why am I seeing this? An independent provider, selected by coverage match and 30-day directory demand. No vendor can pay for this spot.

Hollanders Consultancy
Hollanders Consultancy helps organizations strengthen information security and IT governance through pragmatic advisory, architecture, and compliance support, including ISO 27001, NIS2, risk management, and secure cloud solutions.
Service Type
Regions

SrivelEnterprise
A seasoned professional with 17+ years of fruitful experience with expertise in ISO Certification, SSAE18 (SOC1 and SOC2), GDPR, Quality Management System (ISO 9001), Information Security Management System (ISO 27001), Information Technology Service Management System (ISO 20001), Asset Management System (ISO 55001), HIPAA, Certified Data Protection Officer, Business Continuity, VAPT, Risk Management, Secure Coding, Data Privacy, Processing Integrity, E-learning, Training and Mentoring, Design Thinking, Operations, Strategy, People Management, Technocommercial Acumen. Management Systems: Effectively implemented, maintained, audited ISO 9001 (QMS), ISO 27001 (ISMS), ISO 23001 (BCMS), ISO 20001 (ITSM), ISO 27701 (PMS), ISO 42301 (AIMS), CMMI, SSAE18 (SOC1, SOC2), HIPAA, HITRUST, HITECH, CCPA, GDPR, FedRAMP standards in various organizations across industries. Strong understanding of business best practices w.r.t. quality, information security, continuous process improvements.
Service Type
Regions
Reisender
Reisender helps your organization stay protected while driving performance and growth by assessing risks, implementing ISMS requirements, identifying opportunities, and implementing tailored solutions aligned with business goals.
Service Type
Regions
ReadySecGo
ReadySecGo provides practical, end-to-end information security and compliance services designed for startups and growing organizations. We specialize in ISO 27001, SOC 2, and BSI C5 implementation, readiness, and auditing — helping teams build trust through structured, scalable, and cost-effective security programs. Our services include Gap Assessments, Internal & External Audits, Audit Readiness, and vCISO (Virtual CISO) support. With a hands-on, no-nonsense approach, ReadySecGo bridges the gap between frameworks and real-world execution — enabling companies to achieve compliance maturity without the complexity.
Service Type
Regions
GRCC Jahn
Governance, Risk & Compliance consulting by Viktor Jahn. One point of contact from start to finish. Audits, advisory, and training across NIS2, BISG, TISAX, DORA, GDPR, and ISO 27001. Pragmatic, hands-on and built for practice.
Service Type
Regions
CK Associates
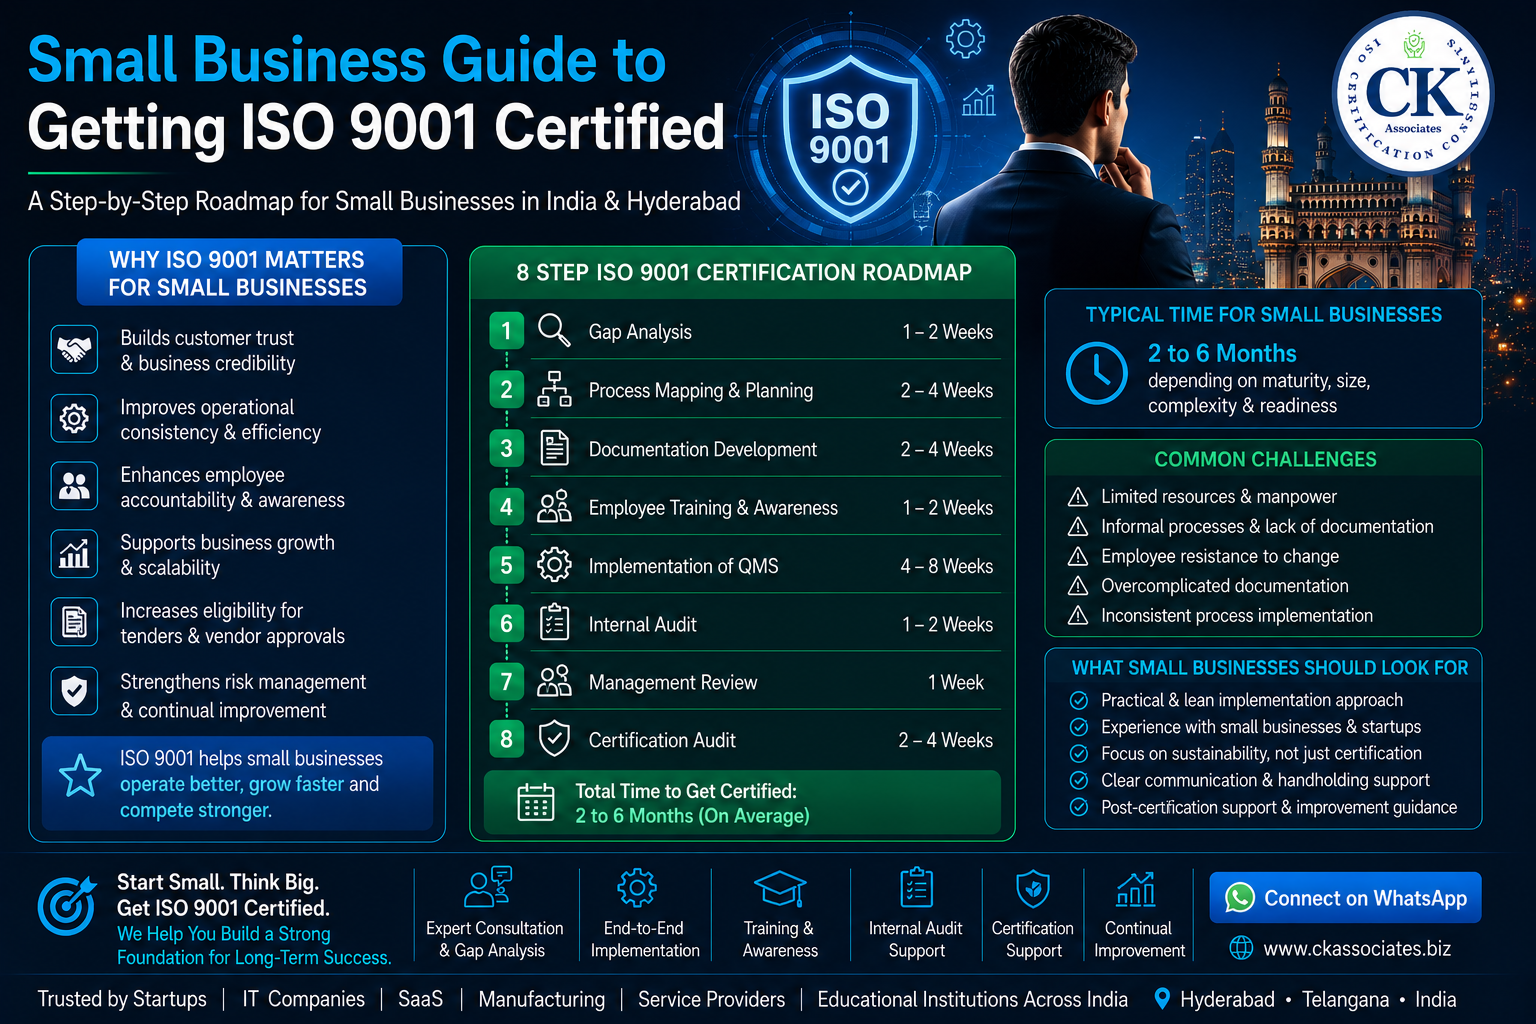
CK Associates is a leading ISO consulting firm with 20+ years of experience and 450+ successful certification projects. We help organizations implement, audit, and achieve ISO standards, including ISO 27001, ISO 42001, ISO 9001, and other compliance frameworks.
Service Type
Regions