Top PCI DSS Compliance-Services – Europa
Compare 12 verified PCI DSS specialists serving Europe. From consultants to certification bodies, find the right partner for your compliance journey. As of October 2026, ISMS Directory lists 12 verified providers for this search, ranked by real 30-day buyer demand on the directory (not paid placement).
Zeige 12 Dienste
i.s.c. Group
ISMS implementations, OneCompliance(tm) program to implement multiple standards at once.
Service Type
Regions
TrustBound GRC
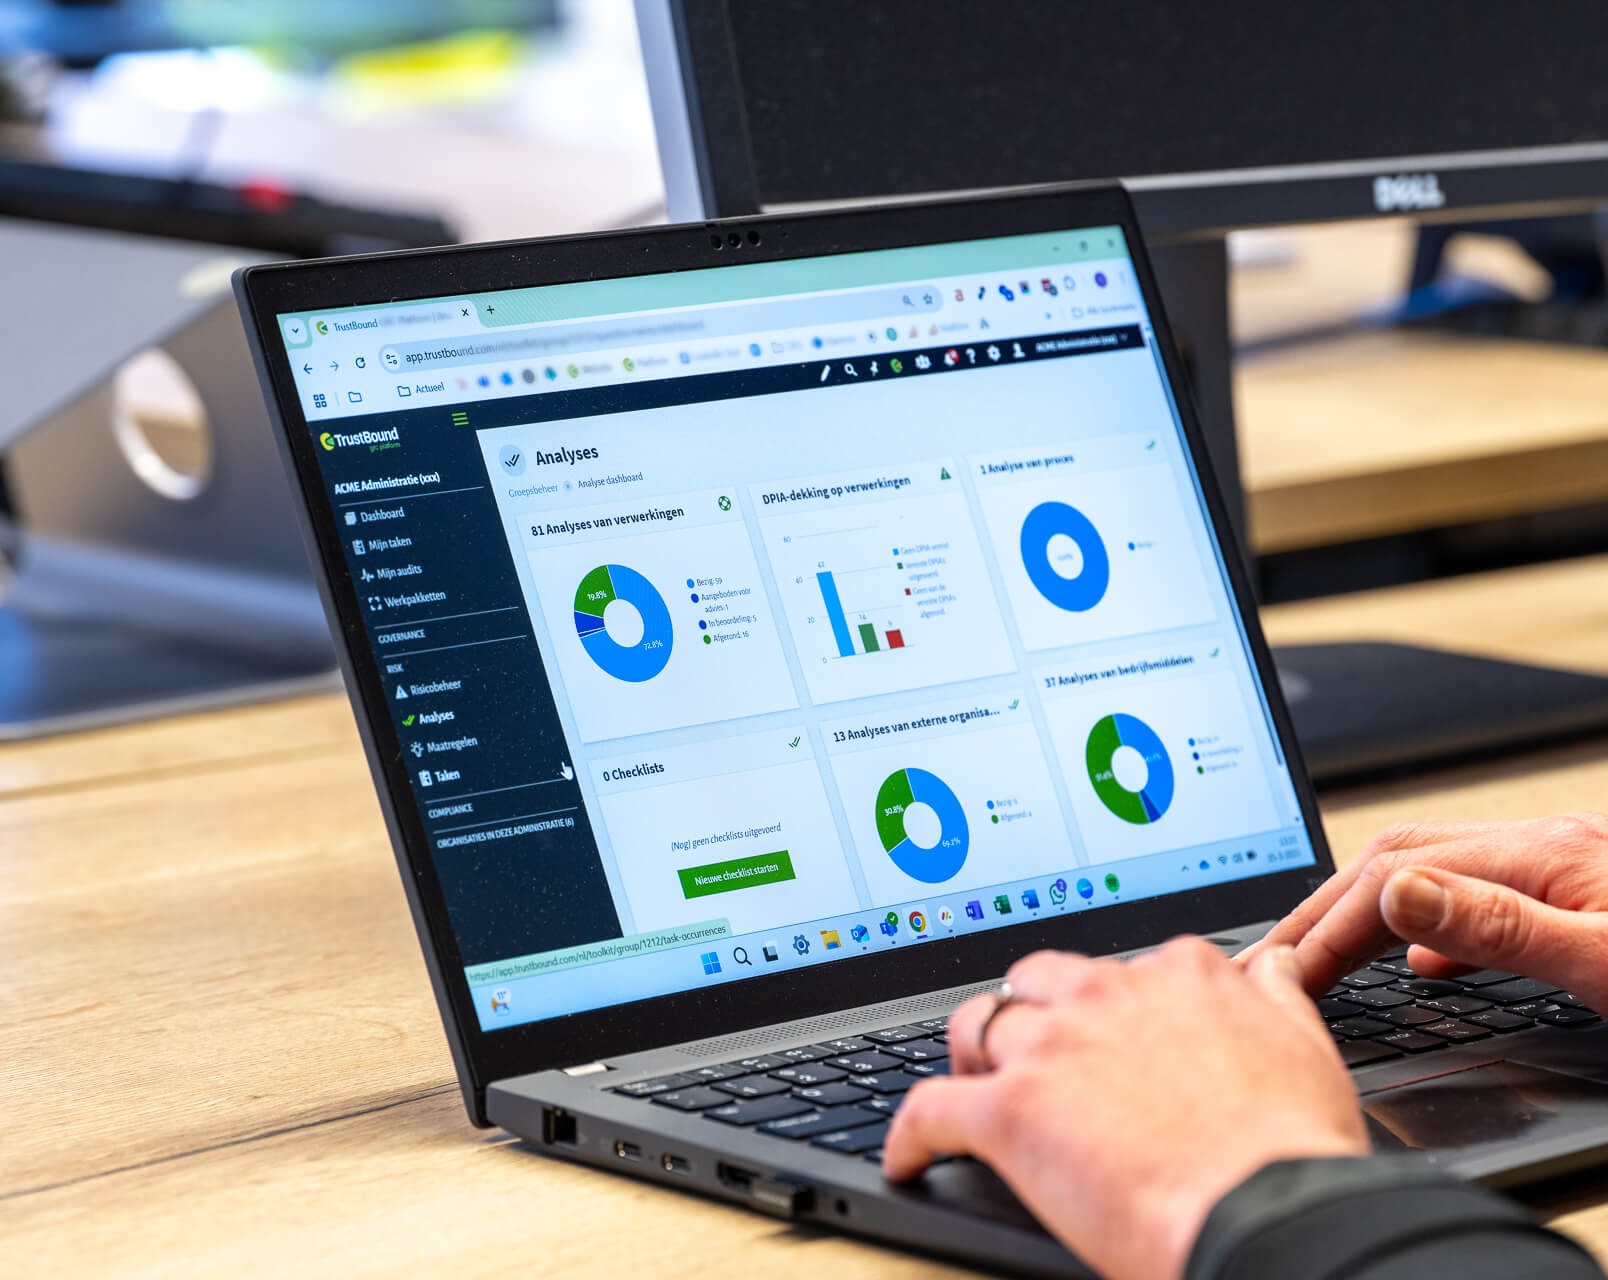
TrustBound GRC is an intuitive platform for information management, privacy, and audit. With smart automation and mappings, it helps organizations gradually improve their compliance. First-line employees receive manageable tasks, while the second line gains oversight and generates clear reports.
Service Type
Regions
Corelink
ISO/IEC 27001 internal audit, ISMS readiness, and ISMS documentation services to support certification and continual improvement.
Service Type
Regions
Hard2bit
Madrid cybersecurity firm offering GRC consulting for ISO 27001, NIS2, DORA, and ENS alongside technical security services.
Matched on: PCI DSS · Europe
Why am I seeing this? An independent provider, selected by coverage match and 30-day directory demand. No vendor can pay for this spot.

LowerPlane
LowerPlane is a compliance automation platform that helps growing companies achieve SOC 2, ISO 27001, GDPR, and HIPAA faster — with continuous monitoring, policy automation, and custom review workflows.
Service Type
Regions
URM Consulting
UK information security consultancy for ISO 27001 implementation, internal audit, and certification support with a large public track record.
Service Type
Regions
GRC Solutions
UK cyber security and compliance group (formerly IT Governance) for ISO 27001 consultancy, training, toolkits, and multi-framework programs.
Service Type
Regions
A-LIGN
High-volume multi-framework audit firm for SOC 2, ISO 27001, HITRUST, FedRAMP, CMMC, and PCI, with dual ANAB/UKAS ISO pathways.
Service Type
Regions
Bitsecura
*** Helping Businesses Achieve Compliance & Certification Success *** Bitsecura is a IT governance, risk, and compliance (GRC) firm specialising in helping organisations protect their critical assets, navigate complex regulatory landscapes, and build sustainable cybersecurity frameworks. With over 20 years of industry experience, we offer strategic guidance, bespoke solutions, and operational support that align seamlessly with your business objectives. Our commitment to practical innovation and long-term partnerships ensures that working with Bitsecura not only strengthens your current security posture, but also builds a lasting foundation for future resilience.
Service Type
Regions

Kordon
Kordon is a straightforward GRC (Governance, Risk, and Compliance) platform designed to simplify compliance processes for companies by offering a comprehensive suite of tools for risk management and regulatory adherence.
Service Type
Regions
Circl3.tech
Circl3.tech is a Cyprus-based cybersecurity advisory firm specialising in vCISO services, information security governance, risk management, and regulatory compliance. Founded by Panos Panayiotou — an ISO/IEC 27001 Lead Implementer (Senior) and seasoned CISO with over 25 years of experience across banking and government sectors — Circl3.tech supports public and private sector organisations in designing and implementing cybersecurity frameworks, ISMS control environments, and strategic security programmes aligned with ISO/IEC 27001 and NIS requirements.
Service Type
Regions
Schellman
Leading US IT compliance attestation firm for SOC 1/2/3, PCI, and ANAB-accredited ISO certifications including ISO 27001 and ISO 42001.
Service Type
Regions